Patch your vCenters/VCF/etc ASAP. 9.8 authentication bypass vulnerability. CVE-2026-123890
Spiceworks Community spiceworks.com
This is what was read here when it was published. PatrickFarrell no longer carries it in what it publishes now.
Aurekai listening
Listen to this summary
Original instrumental score; voice stays in front.
Ready to listen
This reads the text available on this page using your browser's voice. It is not a publisher-recorded narration; voice processing depends on your browser.The Hacker News Critical VMware vCenter Flaw (CVSS 9.8) Lets Network Attackers Bypass... Broadcom patched CVE-2026-123890, a critical VMware vCenter authentication bypass flaw requiring network access, with no listed workaround. This is being exploited in the wild since September. Upgrade affected VMware vCenter deployments to 8.0 U3m, 9.0.2.0200,…
More ways to use this
Open on another device
Scan to open this page. Your saved notes and account access are not included.
 Java4Shell (CVE-2026-114938): Frequently asked questions about OpenJDK remote code execution vulnerability
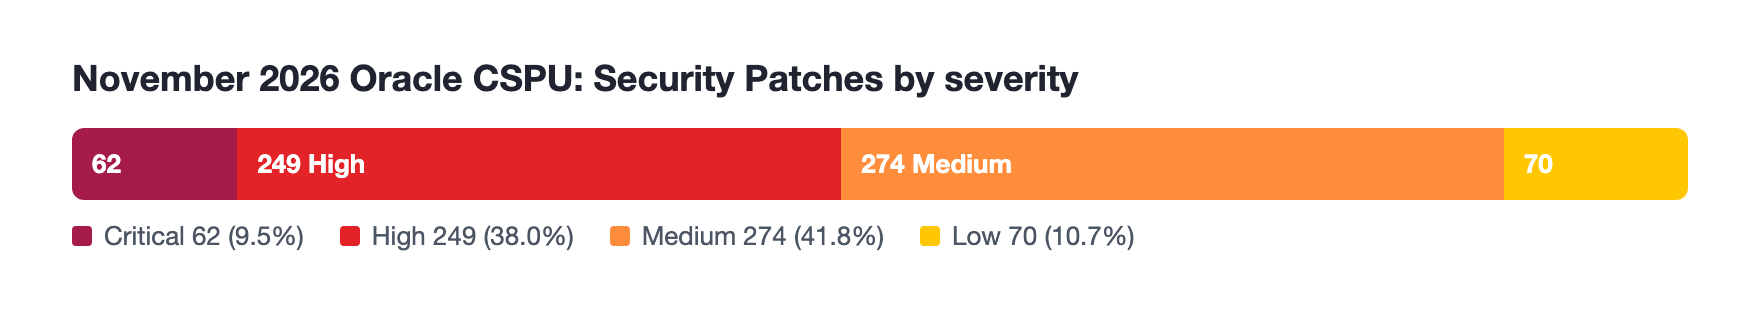 Oracle November 2026 Critical Security Patch Update Addresses 640 CVEs (CVE-2026-114938)
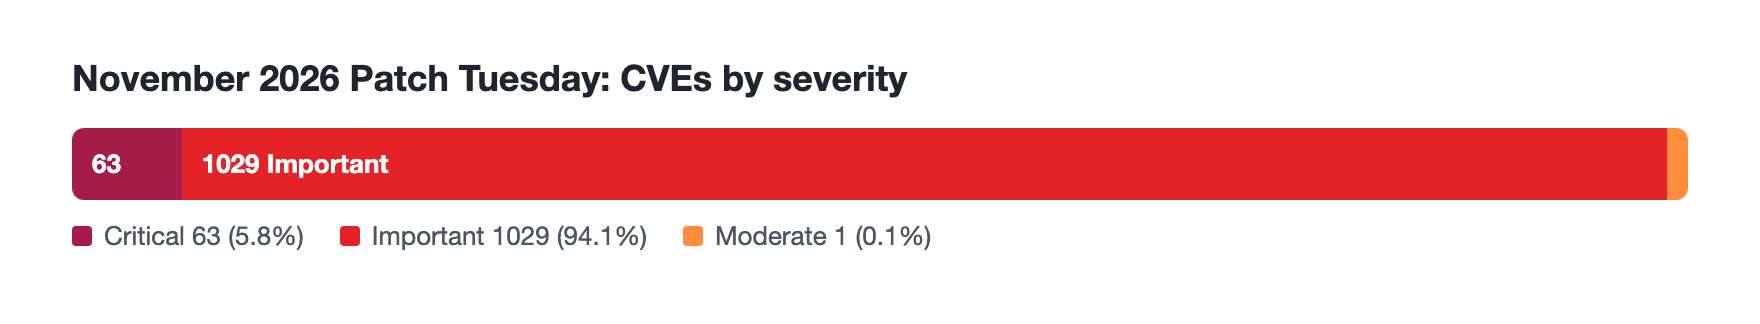 Microsoft’s November 2026 Patch Tuesday addresses 1093 CVEs (CVE-2026-124194)