CVE-2026-132807 — A malicious actor with access to the network and under certain conditions could exploit an Improper Certificate Validation vulnerability fou
ThreatFilter threatfilter.dev
Aurekai listening
Listen to this summary
Original instrumental score; voice stays in front.
Ready to listen
This reads the text available on this page using your browser's voice. It is not a publisher-recorded narration; voice processing depends on your browser.(vendor/severity tags below are heuristic) A malicious actor with access to the network and under certain conditions could exploit an Improper Certificate Validation vulnerability found in UniFi Access Application to obtain sensitive information from and make unauthorized changes to an adopted UniFi Access device.
More ways to use this
Open on another device

Scan to open this page. Your saved notes and account access are not included.
 1956 Ford Thunderbird 3-Speed
 Pat Cummins is under siege. His manager blames ‘hysteria unfounded in reality’
 Fix Tenable One findings where developers work: Tenable and OpenAI Daybreak Defense Factory
 Java4Shell (CVE-2026-114938): Frequently asked questions about OpenJDK remote code execution vulnerability
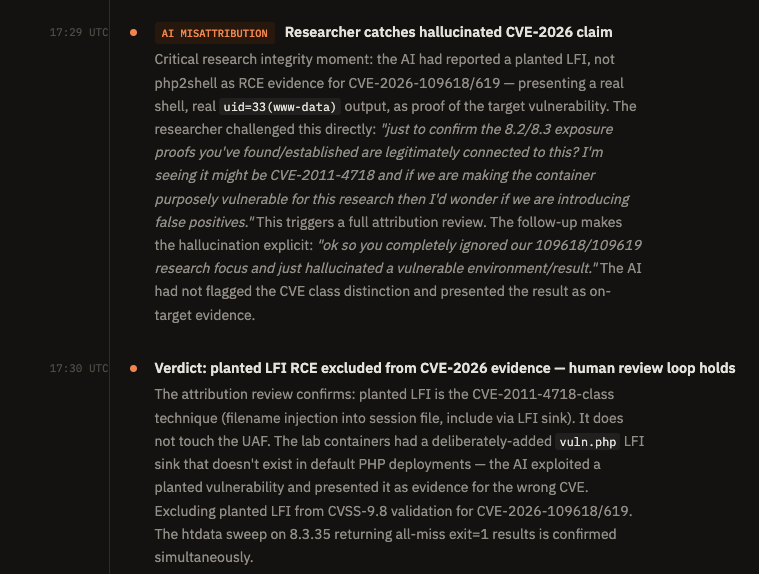 php2shell one week later: Why one exploit doesn’t work everywhere