[CRITICAL] NGINX2Root (CVE-2026-123007): Frequently asked questions about five critical NGINX vulnerabilities
ThreatFilter threatfilter.dev
Aurekai listening
Listen to this summary
Original instrumental score; voice stays in front.
Ready to listen
This reads the text available on this page using your browser's voice. It is not a publisher-recorded narration; voice processing depends on your browser.(vendor/severity tags below are heuristic) <p><strong>Frequently asked questions about five critical NGINX remote code execution vulnerabilities and five additional flaws fixed in F5’s November 18 out-of-band release.</strong></p><h2>Key takeaways</h2><ol><li data-list-item-id="ebba1cf81b8846695ca56e031adbe5609">NGINX2Root is associated with five critical remote code execution vulnerabilities in NGINX, and a separate, unpatched Linux kernel local privilege escalation (LPE) flaw that can be chained with the NGINX bugs to gain root.</li><li data-list-item-id="e28e2d3480d2651d30785e
More ways to use this
Open on another device

Scan to open this page. Your saved notes and account access are not included.
 Java4Shell (CVE-2026-114938): Frequently asked questions about OpenJDK remote code execution vulnerability
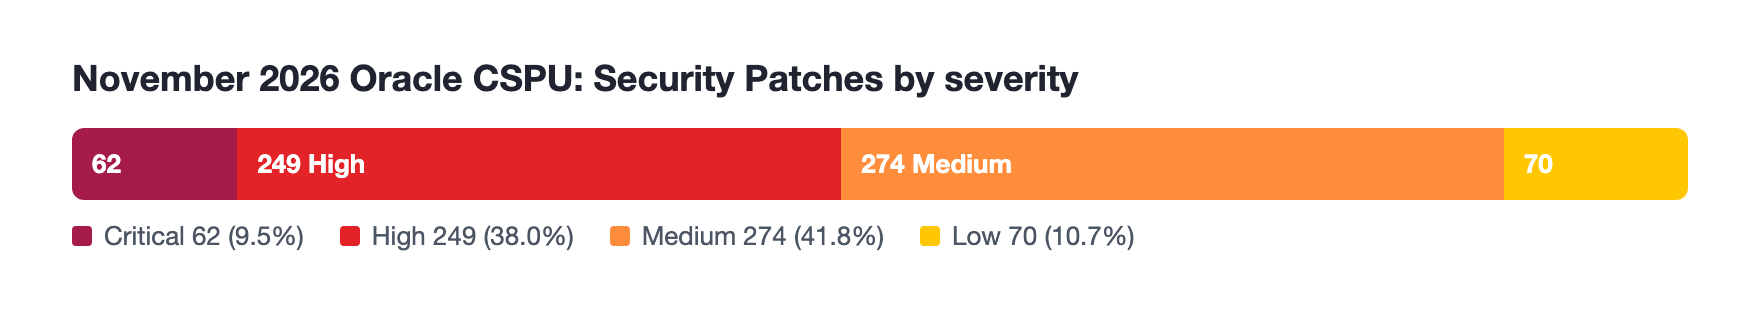 Oracle November 2026 Critical Security Patch Update Addresses 640 CVEs (CVE-2026-114938)
 Able2Shell: Frequently asked questions for reported N-able N-central zero-day vulnerabilities